
IT Security, Data Protection and Attestations
Compyl was founded and continues to be managed by a team of security and compliance professionals. Security and Data protection for us is not an optional accessory, rather essential for every customer's success. We are committed to protecting your data to the highest standards.
Security Commitment
Security best practices and frameworks change all the time. Compyl has employed both the requirements set forth by SOC2 but also those dictated by Microsoft. We are an Azure shop, hosting data in locations most convenient for our customers while ensuring top-notch security. As a single-tenant platform, we do not share any data with third parties, including any integration or usage data.
Data Handling
All data is captured, stored, and disposed of securely, following information security policies approved by management. Our advanced permission model throughout the platform allows users to control access to their data. Data schemas, organized by module, are available upon request, with over 800 tables available.
Certifications and Attestations
Independent third-party attestations and certifications provide assurance over the control environment in which Compyl performs its services to customers. Our controls are independently verified by third-party and independent IT auditors, maintaining our SOC2 Type 2 attestations.
Architecture
Compyl has been built on Microsoft Azure, considered one of the most secure cloud platforms available. Its security is built on multiple layers, including physical, network, host, application, and data security, ensuring protection at every level. Here’s an overview of its security features:
- Compliance and Certifications
Certifications: Azure holds numerous industry certifications, including ISO/IEC 27001, ISO/IEC 27018, SOC 1, SOC 2, SOC 3, and many more.
Compliance: It adheres to international and regional compliance requirements such as GDPR, HIPAA, FedRAMP, and others, making it suitable for various industries, including finance, healthcare, and government. - Data Protection
Encryption: Compyl has encrypted data both at rest and in transit using strong, non-deprecated encryption standards.
Data residency and sovereignty: Compyl stores data in specific geographic regions, ensuring compliance with data residency requirements. - Identity and Access Management (IAM)
Azure Active Directory (AAD): Offers robust identity and access management, including multi-factor authentication (MFA), conditional access policies, and role-based access control (RBAC).
Privileged Identity Management (PIM): Compyl uses PIM to provide just in time privileged access to critical resources. - Threat Protection
Advanced Threat Protection (ATP): Monitors and defends against threats across Azure services.
Azure Security Center: Provides continuous monitoring, security recommendations, and threat detection to secure cloud workloads. - Network Security
Virtual Network (VNet): Isolates and secures resources within a virtual network.
DDoS Protection: Built-in DDoS protection at the network level to mitigate distributed denial-of-service attacks.
Firewalls and NSGs: Azure Firewall, Network Security Groups (NSGs), and Web Application Firewalls (WAFs) help secure and control network traffic. - Operational Security
Patch Management: Regular updates and patches are applied to the platform and underlying infrastructure.
Logging and Monitoring: Azure provides extensive logging and monitoring through services like Azure Monitor, Azure Sentinel, and Log Analytics. - Physical Security
Microsoft data centers have robust physical security measures, including biometric access controls, surveillance, and 24/7 security personnel. - Shared Responsibility Model
Azure operates on a shared responsibility model. While Microsoft secures the infrastructure, Compyl is responsible for securing their data, applications, and network configurations within Azure.
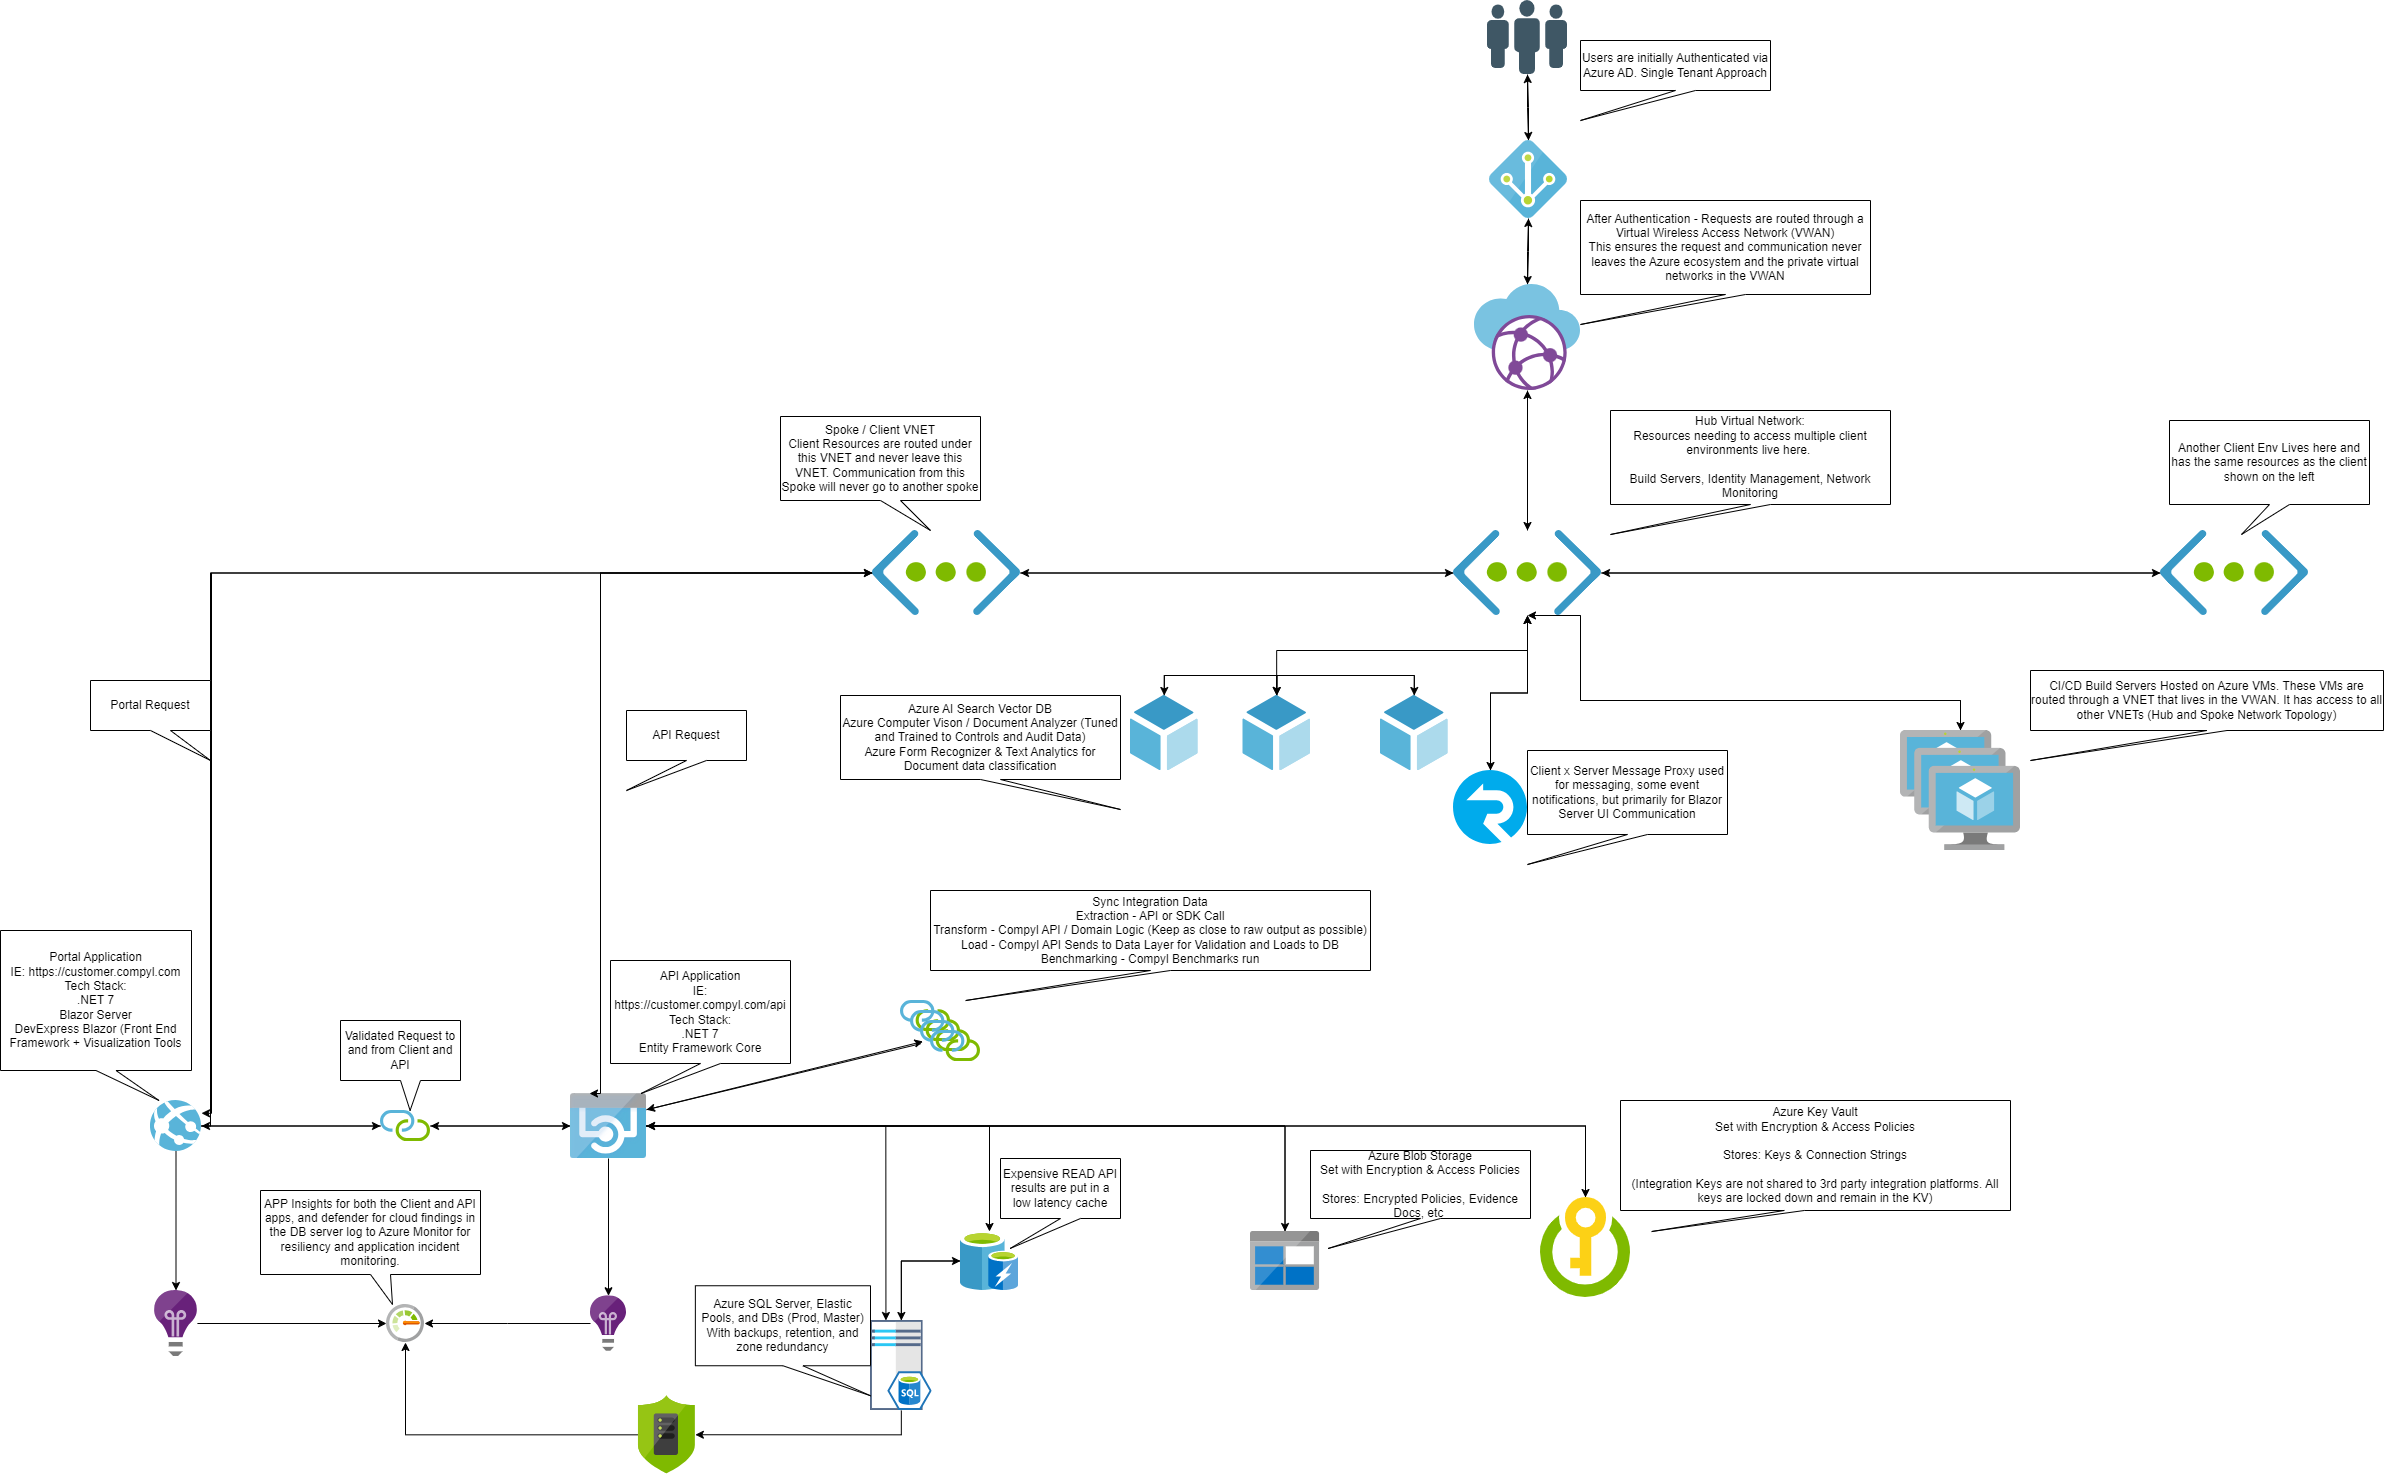
Low level view of Compyl implementation on Azure services
Artefacts
Don't take our word for it, contact us for our latest Pen Test and SOC 2 Type 2 attestations!
The information contained within this blog post details our current/projected development plans. Please note that this information is being shared for INFORMATIONAL PURPOSES ONLY and does not represent a binding commitment on the part of INFOSECTOOLKIT INC. This roadmap and the features/products listed within it are subject to change. You should not rely on or use this information to help make a purchase decision about INFOSECTOOLKIT INC products.
Updated 8 days ago